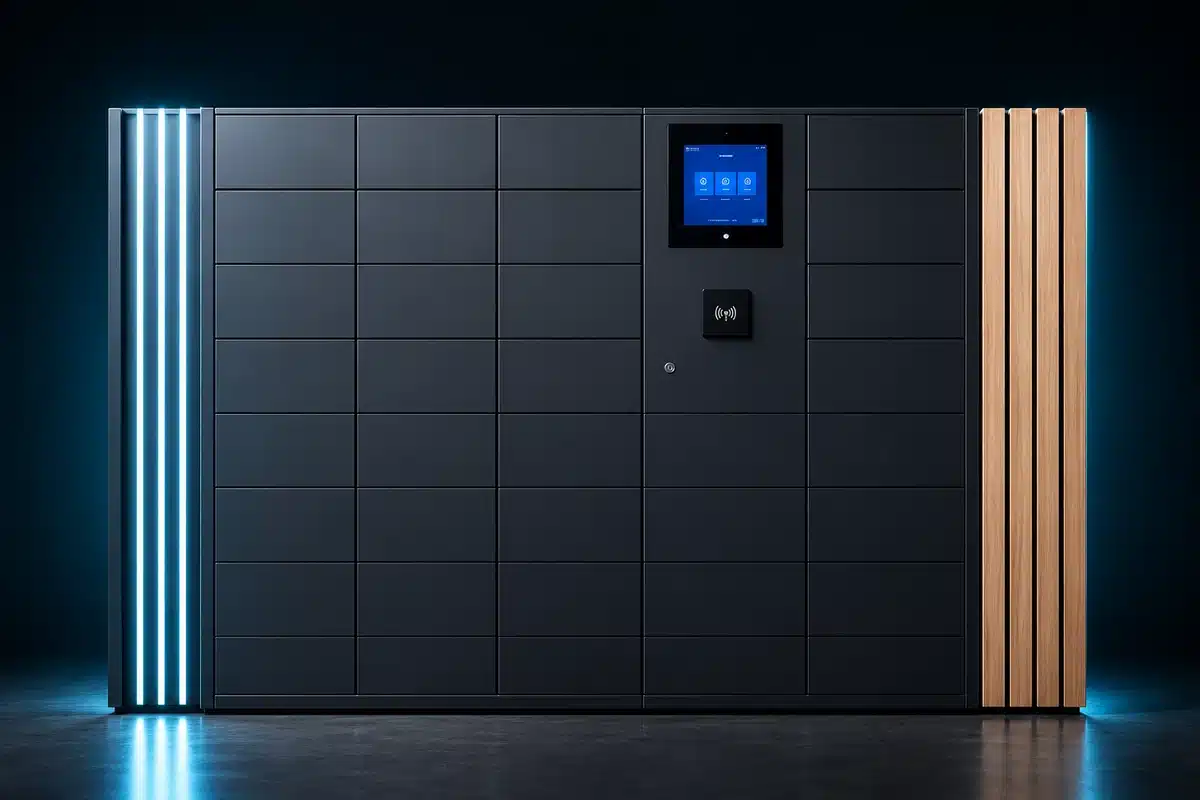
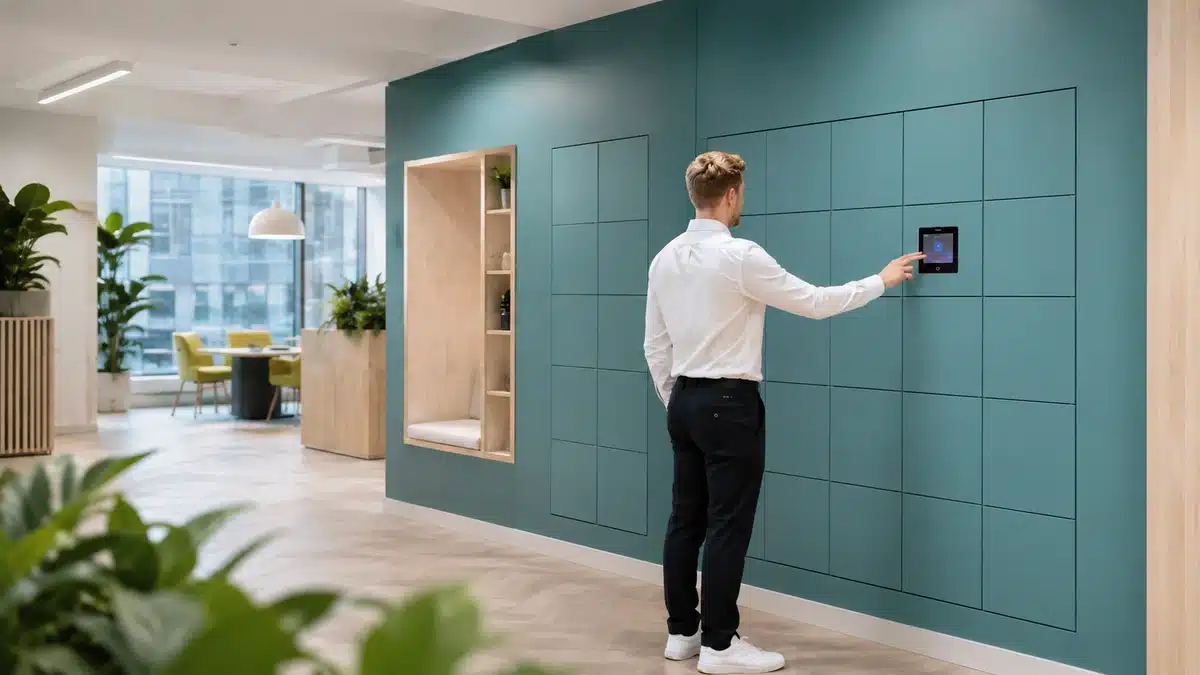
Vflex Smart Lockers, Powered by Keynius, are a state-of-the-art product with quality in-house manufacturing, intelligent design, and a cloud-based platform that can support multiple locker workflows in one smart locker wall.
Vflex Smart Lockers, Powered by Keynius, are a state-of-the-art product with quality in-house manufacturing, intelligent design, and a cloud-based platform that can support multiple locker workflows in one smart locker wall.
Vflex Smart Lockers, Powered by Keynius, are a state-of-the-art product with quality in-house manufacturing, intelligent design, and a cloud-based platform that can support multiple locker workflows in one smart locker wall.
Vflex Smart Lockers, Powered by Keynius, are a state-of-the-art product with quality in-house manufacturing, intelligent design, and a cloud-based platform that can support multiple locker workflows in one smart locker wall.
Global leaders in Smart Lockers & Smart Experiences
We design and deliver integrated systems for streamlined check-ins, secure storage, and enhanced visitor management. Our trusted partner network and focus on sustainability, data security, and customer success drives us to provide the most effective and user-friendly solutions.
Global leaders in Smart Lockers & Smart Experiences
We design and deliver integrated systems for streamlined check-ins, secure storage, and enhanced visitor management. Our trusted partner network and focus on sustainability, data security, and customer success drives us to provide the most effective and user-friendly solutions.
Global leaders in Smart Lockers & Smart Experiences
We design and deliver integrated systems for streamlined check-ins, secure storage, and enhanced visitor management. Our trusted partner network and focus on sustainability, data security, and customer success drives us to provide the most effective and user-friendly solutions.
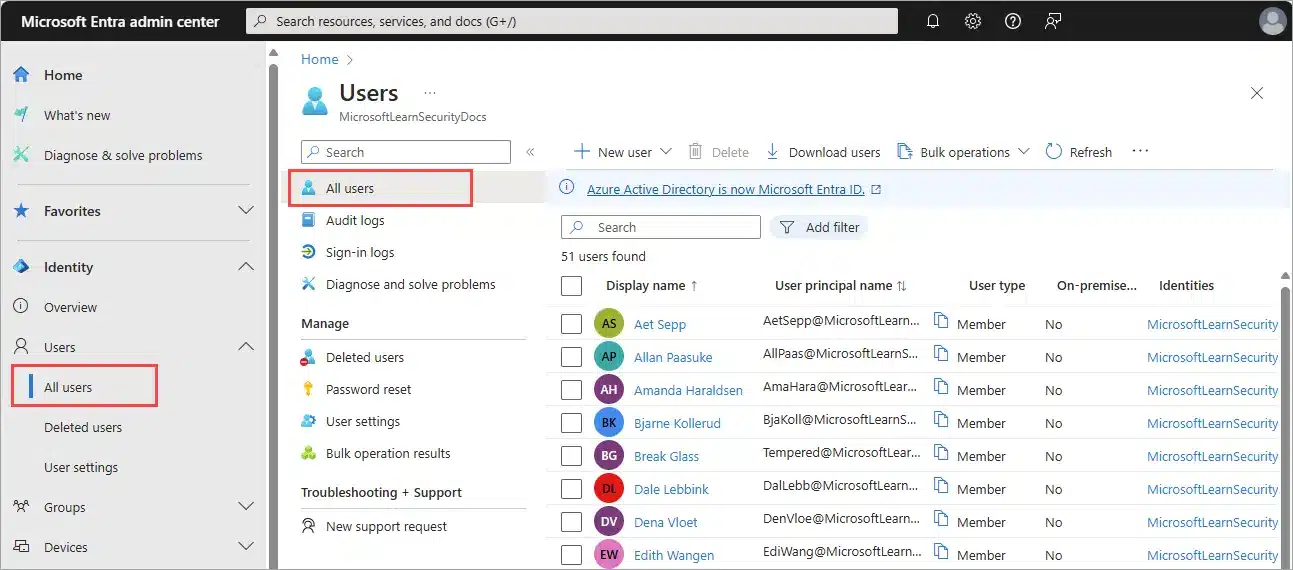
Use company identity to govern who can use which locker.
When somebody joins, changes job or leaves, their approved identity and access rules can inform locker eligibility—without maintaining a separate list of locker users by hand.
Turn “Alex works in IT at London HQ” into a controlled physical action.
The employee should not need a second locker account. The agreed design checks their current company identity and entitlement, then gives a simple result: access allowed, access denied or help required.
♙
One person
Match the locker user to an approved enterprise identity rather than a local name list.
◈
One access decision
Use agreed group, role, site and employment status to decide what the person may do.
The identity-led locker journey
From role change to the right physical access.
This example shows an employee moving into the London IT Support team and becoming eligible to collect shared devices. It is an illustrative design, not evidence of deployed functionality.
MICROSOFT ENTRA ID · ILLUSTRATIVE CHANGE
♙
EMPLOYEE UPDATEDAlex Morgan · IT SupportLondon HQ · group: Device Support
→
VPOD SMART LOCKER
▦
ACCESS AVAILABLEShared-device locker eligibleFloor 3 · employee badge · until role changes
↻
01 · CHANGE
Receive the identity change
A person joins, moves team, changes site or reaches their leaving date.
♙
02 · CHECK
Check current context
The agreed process checks identity, employment status, group, role or location.
✓
03 · ENTITLE
Allow the right locker use
Workplace storage or approved equipment becomes available under the agreed rules.
◈
04 · VERIFY
Confirm the person
The employee uses the agreed badge, phone, PIN or sign-in route at the point of use.
▦
05 · USE
Open, collect or return
Only the permitted door and workflow are available to that employee.
▥
06 · RECORD
Return the agreed event
Access, denial, collection, return or timeout can be passed to the chosen operational record.
!
When identity or access fails
If the employee cannot be matched, belongs to the wrong group, has no suitable locker or loses their credential, deny unsafe access and route the case to the named IT, security or facilities owner.
◎
Running the rules across sites
Keep core identity and offboarding rules consistent while documenting local locker zones, equipment permissions, time windows, emergency processes and support contacts.
Illustrative workflow only. Names, roles, groups, locations and locker outcomes are examples. Supported identity methods, triggers and returned events must be confirmed during solution design.
What each role must decide
Clear ownership from directory to locker door.
IT Directors
Choose the authoritative identity source, provisioning method, support model and records that matter.
Connect the employee, the locker and the operational record.
The Smart Estate Logistics Platform video shows how people interact with storage while the organisation retains visibility of availability and activity.
Agree exactly what identity controls—and what it does not.
Identity source
Confirm the tenant, stable identifier and authoritative joiner, mover and leaver events.
Eligibility rules
Define the groups, roles, locations and approvals that permit each locker workflow.
Authentication
Choose the supported sign-in, badge, phone or PIN route and fallback process.
Events returned
Decide which access, denial, collection, return and timeout events go where.
Deprovisioning
Set timing, retries and emergency revocation for movers, leavers and suspended accounts.
Data and ownership
Document data direction, retention, monitoring, support boundaries and multi-site exceptions.
Integration availability, supported triggers, data direction and delivery scope must be confirmed during solution design. Exact behaviour depends on the agreed Microsoft Entra ID, Vpod and smart-locker configuration. This page does not claim a native connector, certification, commercial relationship, customer deployment or functionality beyond the confirmed project scope.
Start with one identity decision
Show us how a real employee becomes eligible—or loses access—today.
Bring the identity source, sample groups and roles, current locker user process, offboarding timing, event requirements and exception owners.