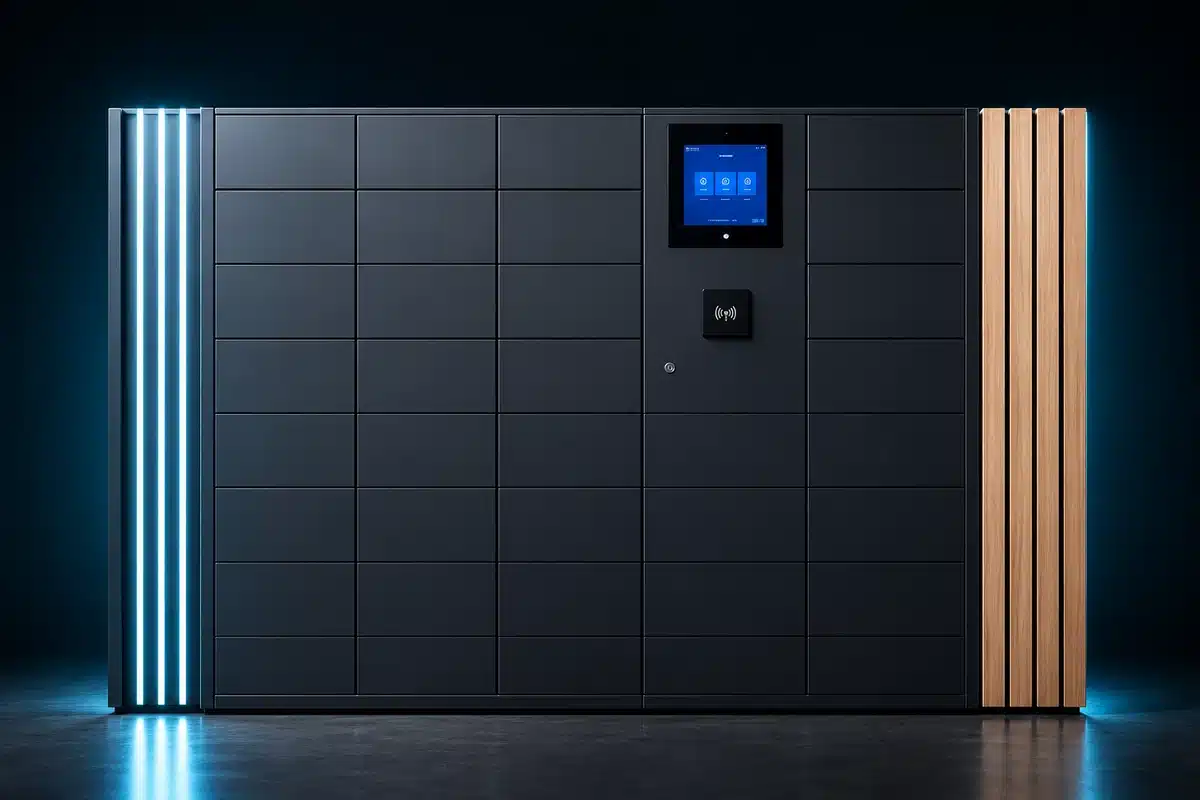
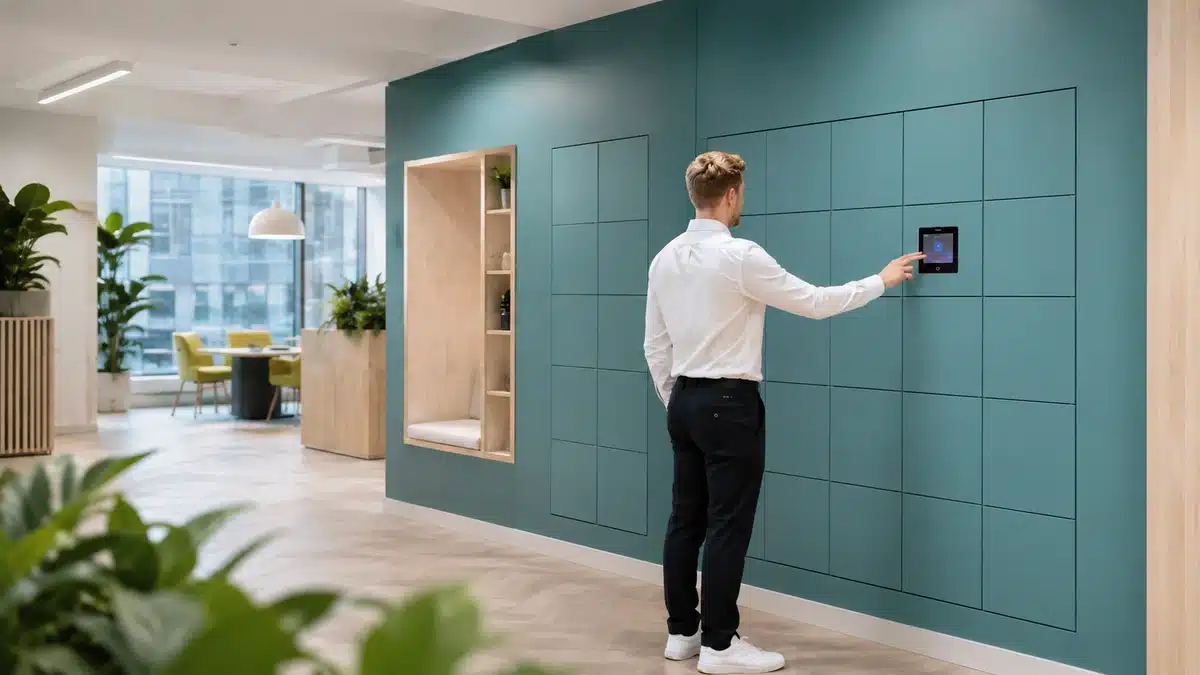
Vflex Smart Lockers, Powered by Keynius, are a state-of-the-art product with quality in-house manufacturing, intelligent design, and a cloud-based platform that can support multiple locker workflows in one smart locker wall.
Vflex Smart Lockers, Powered by Keynius, are a state-of-the-art product with quality in-house manufacturing, intelligent design, and a cloud-based platform that can support multiple locker workflows in one smart locker wall.
Vflex Smart Lockers, Powered by Keynius, are a state-of-the-art product with quality in-house manufacturing, intelligent design, and a cloud-based platform that can support multiple locker workflows in one smart locker wall.
Vflex Smart Lockers, Powered by Keynius, are a state-of-the-art product with quality in-house manufacturing, intelligent design, and a cloud-based platform that can support multiple locker workflows in one smart locker wall.
Global leaders in Smart Lockers & Smart Experiences
We design and deliver integrated systems for streamlined check-ins, secure storage, and enhanced visitor management. Our trusted partner network and focus on sustainability, data security, and customer success drives us to provide the most effective and user-friendly solutions.
Global leaders in Smart Lockers & Smart Experiences
We design and deliver integrated systems for streamlined check-ins, secure storage, and enhanced visitor management. Our trusted partner network and focus on sustainability, data security, and customer success drives us to provide the most effective and user-friendly solutions.
Global leaders in Smart Lockers & Smart Experiences
We design and deliver integrated systems for streamlined check-ins, secure storage, and enhanced visitor management. Our trusted partner network and focus on sustainability, data security, and customer success drives us to provide the most effective and user-friendly solutions.
Carry enterprise access rules through to the locker.
Employee, visitor or contractor access context can inform a separate locker permission, so the right person opens the right door, the activity is recorded and security teams retain central oversight.
Turn an approved person into one permitted locker action.
The user needs a simple result at the locker. Security needs the identity, permission, credential and event kept clear enough to investigate a denial, expiry or unusual activity.
♙
Current person and purpose
Employee, visitor or contractor status provides context for the request.
▥
Visible physical outcome
The selected system records the agreed door, time, user and result.
The access-led locker journey
From contractor approval to Asset Locker A-17.
This example shows a contractor approved to collect test equipment at a London site. It is illustrative and not evidence of deployed functionality.
SIEMENS SIPORT · ILLUSTRATIVE ACCESS APPROVAL
♙
CONTRACTOR AUTHORISEDPriya Shah · Job WO-4812London Campus · Lab Zone · 13 Sep · 10:00–14:00
→
VPOD SMART LOCKER
▦
ASSET READYLocker A-17 assignedTest meter TM-204 · access expires 14:00
▤
01 · APPROVE
Authorise the person or visit
An employee, visitor or contractor receives approval for a defined purpose and period.
⌖
02 · CONTEXT
Check identity and eligibility
Person type, site, zone, job, schedule and current status inform the decision.
✓
03 · ASSIGN
Grant the locker action
An agreed rule permits the correct asset, compartment, collection or return step.
◈
04 · CREDENTIAL
Confirm the person
The user presents the agreed card, token, mobile or other supported credential.
↔
05 · HANDOVER
Collect, use or return
Only the assigned door and permitted action become available.
▥
06 · OVERSIGHT
Return the activity
Agreed access, denial, collection, return or timeout details inform central oversight.
!
When identity, permission or equipment changes
If approval is withdrawn, a credential fails, the asset changes, no compartment is available or collection is missed, keep access secure and route the exception to its named owner.
◎
Governing sites from the centre
Keep identity, permission and reporting rules consistent while documenting each site’s zones, readers, credential technologies, time windows, emergency process and support contacts.
Illustrative workflow only. Names, jobs, credentials, assets, sites and lockers are examples. Supported SIPORT versions, interfaces, triggers, data direction and returned events must be confirmed during solution design.
What each team must decide
Central oversight with clear local responsibility.
Security
Define identity, permission, denial, revocation, investigation and emergency-access rules.
Confirm every boundary before connecting physical access.
SIPORT estate
Identify the exact version, modules, readers, credential types and current architecture.
Identity and approval
Confirm the source for employee, visitor, contractor, role, job and expiry context.
Locker entitlement
Define the asset, zone, compartment, action and time-window rules.
Events returned
Choose which access, denial, collection, return, fault and timeout events go where.
Exception ownership
Name the response team for failed identity, revoked access, missing assets and full lockers.
Governance and sites
Document data direction, retention, monitoring, local differences and emergency operation.
Integration availability, supported triggers, data direction and delivery scope must be confirmed during solution design. Exact behaviour depends on the agreed Siemens SIPORT, Vpod and smart-locker configuration. This page does not claim universal credential compatibility, a native connector, certification, commercial relationship, customer deployment or functionality beyond the confirmed project scope.
Start with one real access journey
Show us how an approved person receives an asset today.
Bring the SIPORT version and architecture, credential types, identity source, asset rules, required events, site differences and common exceptions.